A Red Team in cybersecurity is a group of authorized security professionals who simulate realistic cyberattacks to test an organization’s security defenses. The team works within an agreed scope and uses controlled attack techniques to identify weaknesses across systems, people, processes, and security controls.
Red teaming refers to the activity or approach used to conduct these simulated attacks. Instead of simply looking for individual vulnerabilities, a red team may follow realistic attack paths to understand what an attacker could potentially achieve and whether the organization’s security team can detect and respond to them.
For students and cybersecurity professionals, understanding red teams is useful because the field combines areas such as ethical hacking, penetration testing, network security, web application security, identity security, and incident response.
What Is a Red Team in Cybersecurity?
A Red Team is a group of authorized security professionals who simulate the techniques and behavior of potential attackers during a controlled security assessment.
The term is often used alongside two related concepts:
- Red Team: The people conducting the authorized adversarial activity.
- Red Teaming: The overall activity or approach of simulating an attacker.
- Red Team Assessment: A specific engagement designed to test an organization’s security against defined objectives.
A red team may test technical systems, human behavior, physical security, and the organization’s ability to detect and respond to an attack, depending on the scope of the engagement.
For example, a red team may be given an objective such as determining whether a sensitive system can be reached from an external starting point. The team then works through possible attack paths while following the agreed rules of engagement.
The purpose is not to cause damage. It is to provide the organization with a realistic view of how its security could perform during an attack.
What Does a Red Team Do?
A red team’s activities depend on the objectives and scope of the assessment. Rather than following exactly the same checklist for every organization, the team develops an approach based on the environment it is testing.
1. Reconnaissance
The team gathers information about the target environment. This can include publicly available information, domains, applications, technologies, employee information, and other details relevant to the engagement.
2. Identifying Attack Paths
The team looks for ways an attacker could move from an initial point of access toward the defined objective.
This may involve examining weaknesses in applications, network configurations, identities, endpoints, cloud environments, or other parts of the organization.
3. Controlled Exploitation
Where permitted by the rules of engagement, the team attempts to exploit identified weaknesses to demonstrate what an attacker could achieve.
The objective is to demonstrate realistic security impact without unnecessarily disrupting business operations.
4. Testing Detection and Response
Red teaming is not only about gaining access. The team can also examine whether security controls and defensive teams identify suspicious activity.
This may involve areas such as security monitoring, endpoint detection, logging, alerting, investigation, and incident response.
5. Simulating Attack Techniques
Red teams may use techniques associated with real threat actors, including credential abuse, privilege escalation, lateral movement, phishing, or other forms of adversarial activity where authorized.
Frameworks such as MITRE ATT&CK can also be used to describe and organize adversary tactics and techniques.
6. Reporting the Findings
After the assessment, the red team documents what happened, how the attack path worked, what security controls were encountered, and where improvements may be needed.
The report can help security teams prioritize defensive improvements based on realistic attack scenarios.
How Does a Red Team Assessment Work?
Although every engagement is different, a red team assessment commonly follows a process similar to this:
⁍ Step 1: Define the Objective
The organization and assessment team first establish what the exercise is intended to test.
The objective could involve accessing a specific system, demonstrating exposure of sensitive information, testing physical security, or evaluating the organization’s detection and response capabilities.
⁍ Step 2: Establish Scope and Rules
The scope defines what systems, applications, locations, accounts, and activities are allowed.
Rules are particularly important because red teaming involves realistic attack techniques. Clear boundaries help prevent unnecessary disruption to business operations.
⁍ Step 3: Conduct Reconnaissance
The team gathers information and identifies potential entry points.
Depending on the engagement, this may include external reconnaissance, application analysis, infrastructure discovery, or information about employees and organizational processes.
⁍ Step 4: Simulate the Attack
The team attempts to achieve the agreed objective using realistic attack techniques.
The path may change as the engagement progresses because the team responds to what it discovers instead of simply following a predefined vulnerability checklist.
⁍ Step 5: Evaluate Defensive Visibility
The team observes whether the organization’s security controls detect and respond to the simulated activity.
This can reveal gaps between having a security tool in place and actually detecting meaningful attacker behavior.
⁍ Step 6: Document and Report
The final stage involves documenting the attack path, observations, security weaknesses, defensive gaps, and recommendations for improvement.
The organization can then use these findings to strengthen its security controls and response processes.
Red Teaming vs Penetration Testing
Red teaming and penetration testing are closely related, but they are not always the same type of engagement.
Simulates realistic attacker behavior to test an organization’s overall security. It can involve multiple attack paths and may assess technical, human, and physical security depending on the scope. The focus is often on what an attacker could achieve and whether the organization’s defenses can detect and respond to the activity.
Focuses on identifying and validating security vulnerabilities within a defined technical scope. It commonly examines specific systems, networks, applications, or other assets to determine whether weaknesses can be exploited.
The distinction is not absolute. A penetration test can include elements of adversarial simulation, while a red team engagement can use penetration-testing techniques.
The main difference is generally the objective, scope, and way the assessment is designed, rather than simply how long the engagement takes.
Red Team vs Blue Team vs Purple Team
Cybersecurity teams are often described using different colors to explain their roles.
Simulates an authorized attacker to test an organization’s security defenses and identify how realistic attack activity could affect the environment.
Focuses on defending the organization by monitoring systems, detecting threats, investigating suspicious activity, responding to incidents, and improving security controls.
Brings offensive and defensive security activities together. It uses lessons from Red Team exercises to help improve detection, response, and defensive capabilities.
A simple way to remember the difference is:
Red = simulate the attacker
Blue = defend against the attacker
Purple = improve security through collaboration
What Areas Can a Red Team Test?
The areas tested depend on the organization’s objectives and the agreed scope.
A red team assessment may involve:
- Network infrastructure
- Web applications
- APIs
- Cloud environments
- Identity and access management
- Active Directory
- Endpoints and workstations
- Email security
- Social engineering
- Physical security
- Security monitoring
- Incident detection and response
- Authentication and access controls
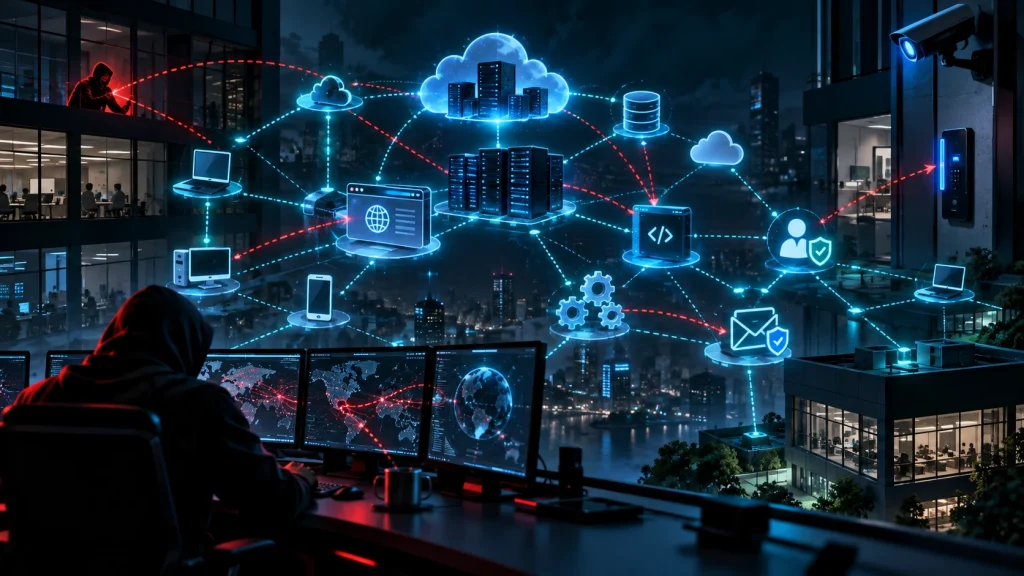
Modern organizations depend on interconnected systems, identities, cloud services, applications, and third-party platforms. As a result, a realistic attack may involve several areas rather than a single vulnerable system.
What Skills Do You Need to Become a Red Teamer?
Red teaming requires a broad technical foundation. You do not need to master everything at the beginning, but several areas become increasingly important as you progress.
● Networking
Understanding TCP/IP, DNS, HTTP/HTTPS, ports, protocols, routing, firewalls, and network architecture provides an important foundation.
● Linux and Windows
Red teamers regularly work with both Linux and Windows environments. Understanding operating systems, command-line tools, permissions, processes, services, and system administration is important.
● Programming and Scripting
Programming is not necessarily about becoming a full-time software developer. Basic scripting can help automate repetitive tasks and understand how security tools and applications work.
Commonly useful areas include:
- Python
- Bash
- PowerShell
- Basic programming concepts
● Web and Application Security
Understanding how websites and applications work helps when assessing vulnerabilities involving authentication, authorization, input handling, APIs, sessions, and other application components.
● Identity and Active Directory
Many enterprise environments depend heavily on identity systems. Understanding authentication, permissions, Active Directory, credentials, and privilege management becomes particularly useful for advanced red-team work.
● Security Fundamentals
You should understand common vulnerabilities, attack techniques, security controls, authentication, encryption basics, endpoint security, network security, and incident response.
● Problem-Solving
Red teaming is not simply about running tools. A large part of the work involves understanding an environment, connecting individual weaknesses, adapting to obstacles, and finding realistic paths toward an objective.
● Communication and Reporting
Technical findings need to be explained clearly. A red teamer should be able to document what happened and communicate the security impact to both technical and non-technical stakeholders.
How to Become a Red Teamer
Red teaming is generally not an entry-level specialization. Many people enter the field after developing experience in related areas such as ethical hacking or penetration testing.
If you are starting your cybersecurity journey after school, it can be useful to first understand the different routes into ethical hacking and cybersecurity. Our guide on how to become an ethical hacker after 12th covers the education, skills, certifications, and career paths beginners can consider.
A practical learning path can look like this:
Step 1: Learn Networking Fundamentals
Start with networking concepts, protocols, ports, services, and basic network security.
Step 2: Learn Linux and Windows
Become comfortable using both operating systems and their command-line environments.
Step 3: Learn Cybersecurity Fundamentals
Understand common vulnerabilities, authentication, access control, security monitoring, and basic defensive concepts.
Step 4: Learn Ethical Hacking
Study how attackers discover and exploit vulnerabilities in controlled and authorized environments.
Step 5: Practice in Legal Labs
Use cybersecurity labs, virtual environments, and intentionally vulnerable systems to develop practical skills safely.
Step 6: Learn Penetration Testing
Understand how security assessments are planned, conducted, documented, and reported.
Step 7: Develop Advanced Offensive Skills
Progress into areas such as Active Directory, web application security, cloud security, privilege escalation, lateral movement, and adversary simulation.
Step 8: Build Practical Experience
Hands-on projects, security assessments, labs, internships, and professional experience can help develop the problem-solving skills required for offensive security work.
Step 9: Consider Relevant Certifications
Certifications can support structured learning and demonstrate knowledge, but practical skills and hands-on experience remain important for offensive security roles.
What Careers Can Red Teaming Lead To?
Learning red-team skills can support several offensive and security assessment career paths, including:
- Penetration Tester
- Red Team Operator
- Offensive Security Analyst
- Security Consultant
- Adversary Simulation Specialist
- Security Assessment Analyst
The exact responsibilities vary between organizations. Some roles focus heavily on penetration testing, while others involve broader adversary simulation and security validation.
Is Red Teaming the Same as Ethical Hacking?
Not exactly.
Ethical hacking is a broad term for authorized security testing and security research conducted with permission.
Red teaming is a more specific approach that attempts to simulate realistic adversarial behavior against an organization’s defenses.
A red team may use ethical hacking and penetration-testing techniques as part of an engagement, but the overall exercise can involve broader objectives and attack paths.
For someone starting their cybersecurity career, learning ethical hacking fundamentals can therefore provide a useful foundation before moving into more specialized red-team work.
Why Do Organizations Use Red Teaming?
Organizations use red teaming to understand how their security performs under realistic attack conditions.
A red team exercise can help identify:
- Attack paths that may not be obvious from individual vulnerability assessments
- Weaknesses in security controls
- Gaps in monitoring and detection
- Problems with identity and access controls
- Opportunities for attackers to move between systems
- Weaknesses in incident response processes
- Differences between expected and actual defensive capabilities
The value comes from connecting these findings into a realistic attack scenario rather than looking at every security issue in isolation.
What Are the Limitations of Red Teaming?
Red teaming is useful, but it does not replace other security activities.
A red team assessment is limited by its:
- Scope and rules of engagement
- Defined objectives
- Available time and resources
- Systems included in the assessment
- Techniques permitted during the exercise
A red team also cannot guarantee that every possible vulnerability or attack path will be discovered.
Organizations still need other security practices such as vulnerability management, penetration testing, secure development, security monitoring, incident response, and regular security assessments.
Is Red Teaming Suitable for Beginners?
Red teaming can be a long-term specialization rather than the first cybersecurity role for many learners.
Beginners can start by building a strong foundation in:
Networking → Linux & Windows → Cybersecurity Fundamentals → Ethical Hacking → Penetration Testing → Adversary Simulation → Red Teaming
You do not need to learn every advanced technique immediately. Building strong fundamentals and gaining practical experience step by step is more useful than trying to learn every red-team tool at once.
How Red Teaming Fits Into Modern Cybersecurity
Organizations today operate across websites, APIs, cloud platforms, endpoints, identity systems, SaaS applications, and interconnected networks.
This means a realistic attack may involve multiple stages across different environments.
For example, an attacker might begin with an exposed application, obtain access to an account, escalate privileges, move to another system, and eventually attempt to reach sensitive information.
Red teaming helps organizations examine these kinds of attack paths in a controlled environment.
Frameworks such as MITRE ATT&CK can also help security professionals describe adversary techniques consistently and connect offensive testing with defensive detection and threat-hunting activities.
Start Building Your Cybersecurity Skills
If you are interested in red teaming, start with the fundamentals rather than focusing only on advanced attack techniques.
Build your understanding of networking, Linux, Windows, cybersecurity concepts, ethical hacking, and penetration testing. Then gradually move toward areas such as Active Directory, web security, cloud security, adversary simulation, and security operations.
A structured cybersecurity course in India can provide a learning path, practical labs, and guided training while you build these skills.
Red teaming is ultimately about more than finding vulnerabilities. It requires understanding how different weaknesses can connect together, thinking from an attacker’s perspective, and helping organizations improve their overall security.
Frequently Asked Questions
A Red Team in cybersecurity is a group of authorized security professionals who simulate realistic attacks to test an organization’s systems, people, security controls, and ability to detect and respond to threats.
Red teaming is the activity of simulating realistic adversarial behavior against an organization’s security defenses within an authorized and controlled scope.
A red team conducts authorized activities such as reconnaissance, controlled exploitation, attack-path testing, and other techniques within an agreed scope. The team then documents its findings and reports areas for improvement.
Penetration testing generally focuses on assessing defined technical systems or applications for exploitable vulnerabilities. Red teaming typically uses a broader, objective-driven approach to simulate realistic attacks and may also evaluate detection and response.
A Red Team simulates an authorized attacker, while a Blue Team focuses on defending the organization by detecting, investigating, and responding to threats.
Purple Teaming is a collaborative approach where offensive and defensive security teams work together to use attack simulations and findings to improve security detection and defense.
Start with networking, Linux, Windows, and cybersecurity fundamentals. Then learn ethical hacking and penetration testing, practice in legal labs, build practical experience, and gradually develop advanced offensive security skills.
No. Ethical hacking is a broader term for authorized security testing, while red teaming focuses more specifically on simulating realistic adversarial activity against an organization’s defenses.